Responsible online casino play depends on a sophisticated technical infrastructure spanning real-time data analytics, automated intervention systems, and cryptographic player verification protocols. Platforms like bitcoin sportsbook and casino Moonbet implement these systems through layered architecture combining session monitoring engines, behavioral pattern recognition algorithms, and mandatory cooling-off mechanisms hardwired into their software stacks. The engineering challenge centers on balancing regulatory compliance requirements with user experience, requiring precise threshold calibration for deposit limits, automated session timers, and self-exclusion databases synchronized across multiple jurisdictions.
At the hardware level, responsible gaming systems rely on secure server infrastructure capable of processing transaction logs in near real-time, with latency targets typically below 100 milliseconds for limit enforcement. Modern implementations incorporate machine learning models trained on millions of gameplay sessions to detect high-risk patterns such as loss-chasing behavior, stake escalation curves, and abnormal session durations. These models feed into interrupt protocols that trigger mandatory breaks, display spend summaries, or temporarily suspend accounts based on configurable risk thresholds.
From a compliance engineering perspective, platforms must integrate with third-party verification services, maintain tamper-proof audit trails, and implement cryptographic methods ensuring that self-exclusion requests cannot be reversed through social engineering or account recovery procedures. This technical framework represents the unglamorous but critical foundation enabling regulated online gaming operations.
The Technical Infrastructure Behind Responsible Gaming Controls
Responsible gaming controls depend on a multi-layered technology stack that spans server infrastructure, database systems, real-time analytics platforms, and interconnected software modules. At the foundation, online-casino platforms typically deploy clustered server architectures with dedicated nodes for transaction processing, gameplay hosting, and behavioral monitoring. This separation ensures that responsible gaming systems operate independently of core gaming functions, preventing performance bottlenecks during peak traffic while maintaining continuous oversight of player activity. High-availability configurations with redundant hardware and load-balancing mechanisms guarantee that protective interventions remain functional even during system failures or maintenance windows.
Database architecture plays a critical role in storing and retrieving player behavior profiles, limit configurations, and historical activity logs. Most platforms implement relational database management systems capable of handling millions of concurrent queries, with separate schemas for player accounts, financial transactions, and behavioral analytics. Time-series databases have become increasingly common for storing sequential gameplay data, as they efficiently index timestamp-based queries needed for pattern detection. Data replication across geographically distributed centers ensures both disaster recovery capability and compliance with regional data sovereignty requirements, while encryption at rest protects sensitive player information from unauthorized access.
Real-time monitoring systems process player activity streams through complex event processing engines that evaluate gameplay against predefined thresholds and behavioral models. These systems ingest data from multiple sources, including bet placement, deposit attempts, session duration counters, and loss accumulators, then route this information through rule engines and machine learning pipelines. The processing latency matters significantly; interventions delayed by even seconds can allow problematic behavior to escalate. Modern implementations achieve sub-second response times by deploying in-memory computing frameworks that maintain active player states without disk I/O overhead.
Integration between these components happens through standardized APIs and message queuing systems that decouple services while maintaining data consistency. Microservices architecture has largely replaced monolithic designs, allowing operators to update individual responsible gaming modules without disrupting core platform operations. This modularity proves essential when regulatory requirements change, as compliance teams can modify limit enforcement logic or add new intervention triggers without full system redeployment. Container orchestration platforms manage these distributed services, automatically scaling monitoring capacity during high-traffic periods when behavioral analysis demands increase proportionally with active player counts.
Software Systems for Player Behavior Monitoring
Modern online-casino platforms deploy multi-layered monitoring systems that combine statistical analysis with machine learning to identify at-risk player behavior before it escalates. These software architectures process thousands of data points per user session, applying algorithmic thresholds calibrated against clinically-validated markers of problem gambling rather than marketing-driven engagement metrics.
The core monitoring pipeline typically runs on dedicated server clusters that capture granular event data, every bet placed, every deposit initiated, session start and end timestamps, game type selections, and navigation patterns within the platform. This telemetry feeds into both rules-based detection engines and adaptive machine learning models. Rules-based systems flag simple threshold breaches: session duration exceeding four consecutive hours, rapid successive deposits within ten-minute windows, or bet size escalation patterns that deviate significantly from a player’s baseline. These rigid checks serve as first-line alerts but generate substantial false positives without contextual interpretation.
Pattern-recognition AI models add crucial behavioral nuance by establishing individual player profiles over time. Supervised learning classifiers trained on anonymized datasets from self-excluded players can detect early-stage risk signatures, such as loss-chasing sequences where bet amounts double after losses, irregular deposit timing that suggests impulsive decision-making, or bimodal session patterns characteristic of escape-driven play. These models run inference in near-real-time, with latency targets under 500 milliseconds to enable intervention before a risky session concludes.
Feature engineering proves critical: raw transaction logs must be transformed into behavioral indicators. Session intensity scores combine bet frequency with stake variance; temporal volatility metrics quantify erratic play schedules; bankroll depletion velocity tracks the rate at which deposited funds deplete relative to expected loss rates for specific game types. Some implementations incorporate graph-based models that analyze sequential decision paths, identifying cognitive patterns associated with tilt states or dissociative play.
The AI acceleration capabilities of modern GPUs and specialized tensor processing units have enabled platforms to deploy ensemble methods, combining gradient-boosted decision trees, recurrent neural networks for sequence analysis, and anomaly detection algorithms, without incurring processing delays that degrade user experience. Model outputs typically feed into a risk-scoring framework that determines intervention type: soft nudges like session reminders at moderate scores, mandatory cool-off periods at elevated thresholds, or staff-initiated outreach for sustained high-risk patterns. Continuous model retraining using feedback from player outcomes and self-reported data helps minimize both missed detections and intrusive false alarms.
Self-Exclusion and Limit-Setting Mechanisms
Self-exclusion and limit-setting mechanisms rely on a multi-layered data architecture where player-defined restrictions are stored in relational databases and enforced through a combination of real-time validation logic and scheduled reconciliation processes. When a player sets a daily deposit limit, this preference is written to a dedicated responsible-gaming table with fields for limit type, threshold value, time window, and activation timestamp. The enforcement occurs at the transaction layer: before processing a deposit request, the system queries cumulative deposits within the current period against the stored limit. If the new transaction would exceed the threshold, the payment gateway receives a rejection flag before fund transfer begins.
| Limit Type | Enforcement Method | Typical Refresh Interval |
|---|---|---|
| Deposit Limit | Database trigger + payment API validation | Real-time per transaction |
| Loss Limit | Application logic polling net position | Every 30-60 seconds |
| Wager Limit | Pre-bet validation in game server | Real-time per bet placement |
| Session Time | Client-side timer + server heartbeat check | Every 5 minutes (server), 1 second (client) |
Session timers present a particular technical challenge because they must survive browser refreshes and device switches. The canonical session start time is recorded server-side when authentication occurs, and elapsed duration is recalculated on each API call. If the player closes their browser and reopens the site within the same calendar day, the original session timestamp persists, preventing simple circumvention by logging out and back in.
Self-exclusion operates at the authentication layer rather than the transaction layer. When a player activates self-exclusion, their account status field transitions to a restricted state that blocks login attempts. The exclusion period, ranging from 24 hours to permanent, is stored alongside the activation date, and the system checks both values during credential validation. Multi-brand operators face the added complexity of propagating exclusions across all owned platforms, typically achieved through a centralized identity service that broadcasts status changes to subsidiary databases via message queues or synchronous API calls.
Cross-platform synchronization remains the most persistent engineering obstacle. A player who sets a weekly loss limit on desktop must see that same restriction honored on mobile, which requires either a centralized limit-tracking service or continuous database replication between application servers. The latter introduces race conditions when near-simultaneous bets occur across devices, making the former approach, where all enforcement logic calls a single authoritative microservice, the current industry standard for operators managing high transaction volumes.
Identity Verification and Age-Gate Technologies
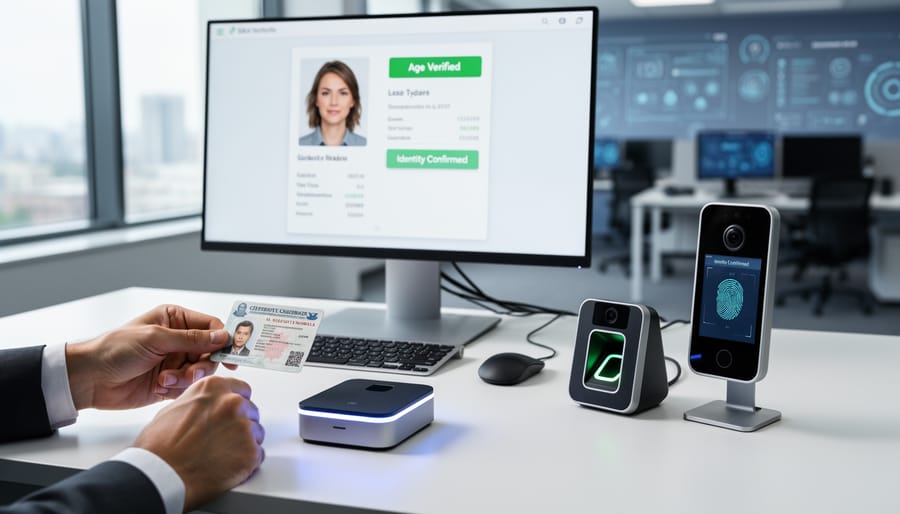
Online-casino platforms deploy multi-layer electronic verification systems to enforce age restrictions and confirm player identities before account activation. These systems combine optical character recognition (OCR) hardware, liveness detection algorithms, and third-party data validators to create a verification pipeline that typically completes in under two minutes while maintaining compliance with KYC (Know Your Customer) regulations.
Document scanning modules form the first verification layer. Mobile-optimized camera interfaces capture government-issued IDs, driver’s licenses, or passports, then feed these images to OCR engines that extract name, date of birth, document number, and expiration date. Modern implementations use edge detection algorithms to assess image quality in real time, rejecting blurry or partially obscured documents before submission. Server-side validation cross-references extracted data fields against known document formats for each issuing jurisdiction, flagging inconsistencies in font rendering, hologram placement, or security feature positioning that suggest forgery.
Biometric verification adds a second authentication factor. Facial recognition systems compare a live selfie capture against the photo embedded in the submitted identity document, using neural networks trained to detect presentation attacks such as printed photos, screen replays, or 3D masks. Liveness checks require users to perform random head movements or blink patterns, with depth-sensing analysis confirming the presence of a physical person rather than a static image. Processing happens either on-platform using proprietary algorithms or through specialized API services that return match confidence scores within 500 milliseconds.
Third-party verification APIs supplement document checks by querying national identity databases, credit bureaus, or electoral registers where legally permitted. These integrations verify that the submitted name and birthdate correspond to a real person at the stated address, with responses encrypted via TLS 1.3 and logged for audit purposes.
Data protection compliance requires careful architecture. Verification systems must meet GDPR requirements for data minimization, storing only essential identity fields and purging biometric templates after initial verification. Access controls limit verification data visibility to compliance personnel only, with all queries logged in immutable audit trails. Platforms operating across multiple jurisdictions implement region-specific verification workflows, adapting document types and data retention policies to local privacy regulations while maintaining a consistent security baseline.
Security Protocols Supporting Responsible Play Enforcement
Protecting responsible gaming systems from tampering or bypass attempts requires defense-in-depth cybersecurity architectures that span multiple layers. End-to-end AES-256 encryption secures data both at rest and in transit, ensuring that player limit settings, self-exclusion records, and behavioral flags cannot be intercepted or altered during transmission between client devices, application servers, and database clusters. Modern platforms implement certificate pinning and secure wireless protocols to prevent man-in-the-middle attacks that could compromise player protection data flows.
Access control systems enforce strict role-based permissions, limiting who can view, modify, or disable responsible gaming features within the platform’s administrative interface. Multi-factor authentication gates access to these critical systems, while hardware security modules (HSMs) store cryptographic keys used for signing responsible gaming transactions, making unauthorized modification computationally infeasible. Separation of duties ensures that no single administrator can alter both the gaming logic and the player protection enforcement layer without independent verification.
Comprehensive audit logging captures every interaction with responsible gaming controls, each limit adjustment, self-exclusion request, and automated intervention trigger, with tamper-proof timestamping provided by cryptographic hash chains or blockchain-anchored records. These logs integrate with audit-ready instrumentation that regulatory bodies and third-party testing labs use to verify system integrity during compliance reviews. Intrusion detection systems monitor for anomalous access patterns that might indicate attempts to circumvent player protection mechanisms, triggering automated alerts and lockouts when suspicious activity occurs. Network segmentation isolates responsible gaming databases from general gaming operations, reducing the attack surface and ensuring that even a breach elsewhere in the platform cannot compromise player protection enforcement.
Common Technical Implementation Challenges and Solutions
Real-time processing latency remains one of the most pressing challenges in responsible gaming enforcement. When a player approaches a preset limit or triggers a behavioral alert, intervention systems must respond within milliseconds to be effective. However, analyzing complex behavioral patterns across multiple data streams introduces processing delays, particularly when machine learning models run inference checks on incoming transaction data. Current solutions employ edge computing architectures that distribute processing closer to the player interface, combined with predictive algorithms that pre-calculate likely intervention points based on historical patterns. This approach reduces decision latency from several seconds to under 200 milliseconds in most implementations.
Multi-device synchronization presents another significant obstacle. A player may access the same account simultaneously or in rapid succession from a desktop, mobile device, and tablet, each maintaining its own local session state. Without real-time synchronization, a player who sets a deposit limit on one device could theoretically bypass it on another before the database updates propagate. Modern platforms address this through distributed state management systems using technologies like Redis or Apache Kafka, which maintain a single source of truth for player limits and session data across all endpoints. These systems employ event-driven architectures that broadcast state changes to all connected devices within 50-100 milliseconds.
Legacy system integration compounds these difficulties, especially for operators running established platforms built on older database schemas not designed with granular responsible gaming controls in mind. Retrofitting real-time monitoring onto monolithic legacy systems often requires middleware layers that translate between old and new data structures, introducing additional points of failure and performance bottlenecks.
How do platforms prevent limit circumvention across devices?
Platforms use distributed state management systems with event-driven architectures to maintain synchronized player limits across all devices. These systems broadcast state changes to all connected endpoints in real time, typically within 50-100 milliseconds.
What latency is acceptable for intervention triggers?
Industry best practice targets under 200 milliseconds for intervention triggers. Edge computing architectures and predictive algorithms help reduce decision latency from several seconds to this acceptable threshold.
How are false positives in behavior detection minimized?
Engineers tune machine learning thresholds based on extensive historical data and implement multi-factor scoring systems that require multiple behavioral indicators before triggering interventions. Regular model retraining with validated datasets helps reduce erroneous alerts.
What happens when responsible gaming systems conflict with marketing automation?
Modern platforms implement priority hierarchies that give responsible gaming controls precedence over promotional systems. When conflicts arise, the player protection logic overrides marketing triggers, and audit logs capture these events for compliance review.
Balancing user experience with protective interventions requires careful engineering judgment. Overly aggressive alert systems generate friction that frustrates legitimate players, while insufficient intervention fails to protect vulnerable users. Engineers typically implement tiered response systems with escalating interventions: soft nudges for minor threshold breaches, mandatory cooling-off periods for moderate concerns, and account restrictions for severe behavioral flags. Machine learning models continuously refine these thresholds using feedback loops that analyze player responses to different intervention types, optimizing the balance between protection and usability.
The integration of electronics, security architecture, and software systems creates the technical foundation that makes responsible gaming policies enforceable rather than aspirational. From real-time behavioral monitoring to multi-layered identity verification, these platforms depend on coordinated hardware and software ecosystems to detect risk patterns, enforce limits, and protect vulnerable players without manual oversight.
The systems examined here, server infrastructure handling millions of transactions, machine learning models parsing behavioral data, cryptographic protocols securing player information, demonstrate that responsible play enforcement is fundamentally an engineering challenge. Effective player protection requires low-latency processing, tamper-proof logging, cross-platform synchronization, and seamless integration of verification APIs, all while maintaining regulatory compliance and user experience standards.
As of 2026, artificial intelligence and advanced analytics are expanding the capability frontier. Neural networks now identify subtle risk indicators that rule-based systems miss, while federated learning approaches enable pattern recognition across operators without compromising data privacy. The ongoing evolution of these technologies will determine whether responsible gaming systems keep pace with increasingly sophisticated platform features and emerging behavioral risks in digital gaming environments.